

Securing Your Identity in 2024: Strong Passwords
As cyber threats evolve into highly automated, AI-driven operations, the tactics required to defend your digital identity must also mature. The methods used five years ago are now dangerously obsolete. To insulate your sensitive financial and personal data, you must adhere strictly to the modern best practices for creating strong passwords and passphrases. By mastering strong passwords, you build an impenetrable defense.
Best Practices for Passphrases (Master Keys)
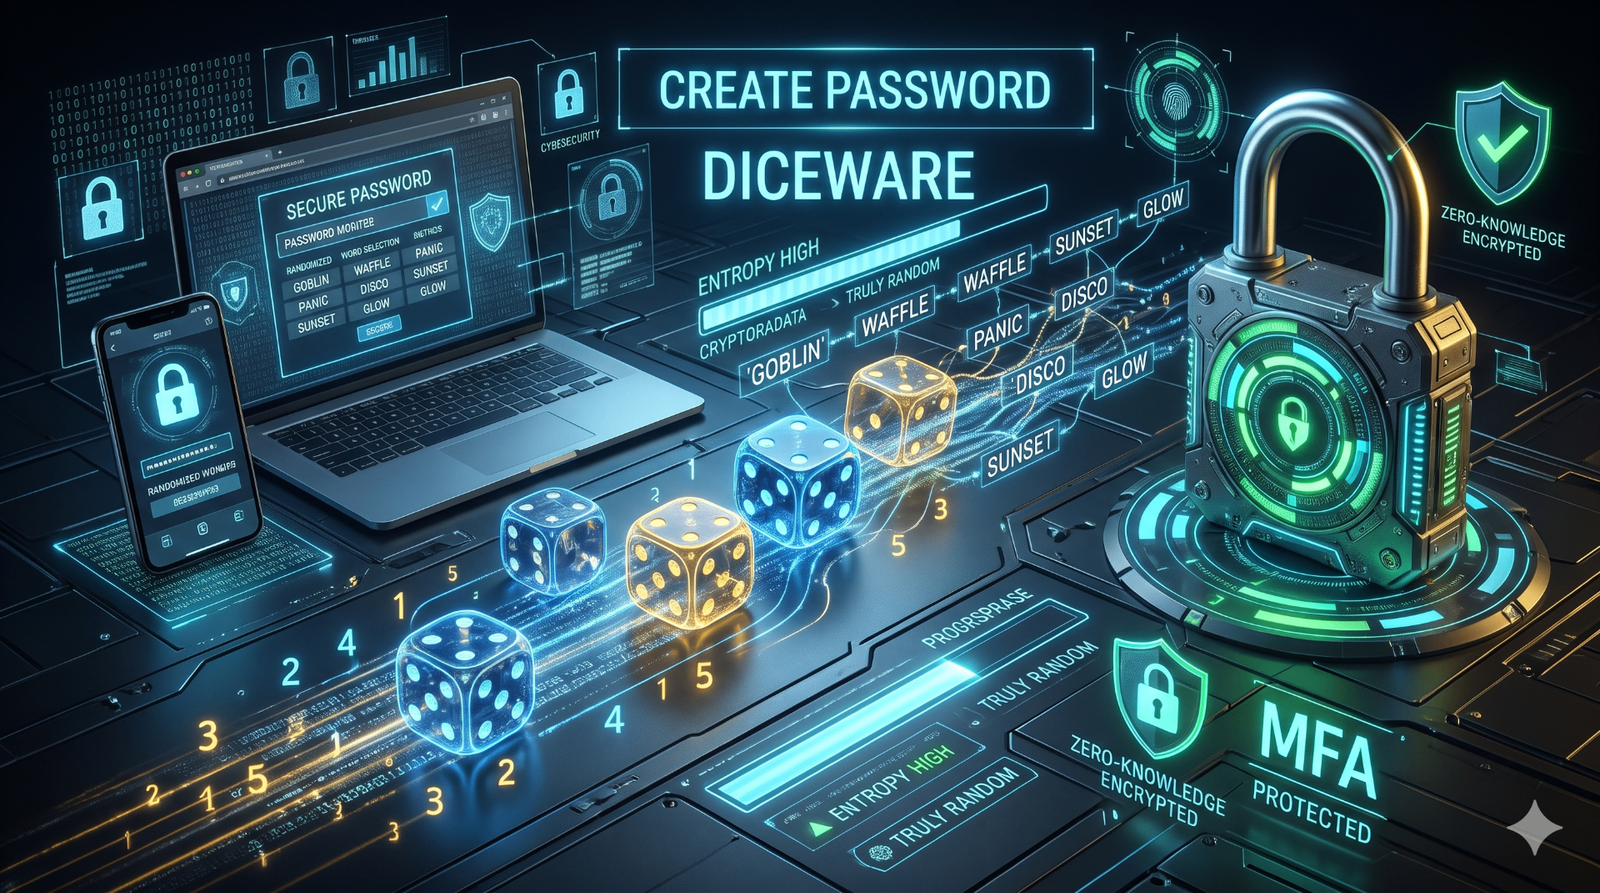
Alongside strong passwords, passphrases should be explicitly reserved for critical access points: device login, full-disk encryption, and password manager vaults.
- Ensure Absolute Randomness: Never invent a phrase yourself. Utilize a secure, offline tool to select words randomly.
- Maximize Word Count: In 2024, four words is the bare minimum. Moving to five or six words is recommended.
- Use Consistent Separators: Separate words with spaces or hyphens to make typing fluid.
Best Practices for Strong Passwords (Auto-Filled Accounts)
For the vast sea of internet accounts you interact with daily, human memory is no longer required. These credentials must be strong passwords handled exclusively by software.
- Absolute Uniqueness: The golden rule is zero reuse. Every portal must possess completely unique strong passwords. Generate them using a strong passwords generator.
- Maximize Cryptographic Density: Produce 24 to 32 characters, utilizing all symbols. Maxing out entropy costs you nothing in usability.
- Client-Side Generation: Only utilize zero-knowledge tools that process strong passwords locally in your browser. Verify them with a strong passwords checker.
Common Security Mistakes to Avoid
Even with robust credentials, poor security hygiene can compromise your defense. Avoid the incremental update trap—changing Password23 to Password24 provides zero enhanced security.
The MFA Requirement for Strong Passwords
In 2024, strong passwords are merely the first layer of defense. Multi-Factor Authentication (MFA) is non-negotiable. Transition away from vulnerable SMS codes to hardware keys or TOTP apps.
Conclusion
Securing your accounts requires rigorous cryptographic standards. Establish passphrases for master access and use strong passwords for everything else to render your identity unassailable.

Leave a comment
Comments are moderated before appearing. Please keep it respectful and on-topic. Your email is required for verification but is never displayed publicly or shared.